Many small and midsized businesses believe account-takeover risk is addressed once multi-factor authentication is enabled. That assumption is understandable—and increasingly dangerous.
Huntress reported a 155-fold increase in password-spraying attacks during the first half of 2026, including a campaign that generated more than 81 million login attempts in two weeks. The attackers targeted Microsoft cloud environments through an authentication path associated with Azure CLI, Microsoft’s command-line management tool for Azure and Entra resources.
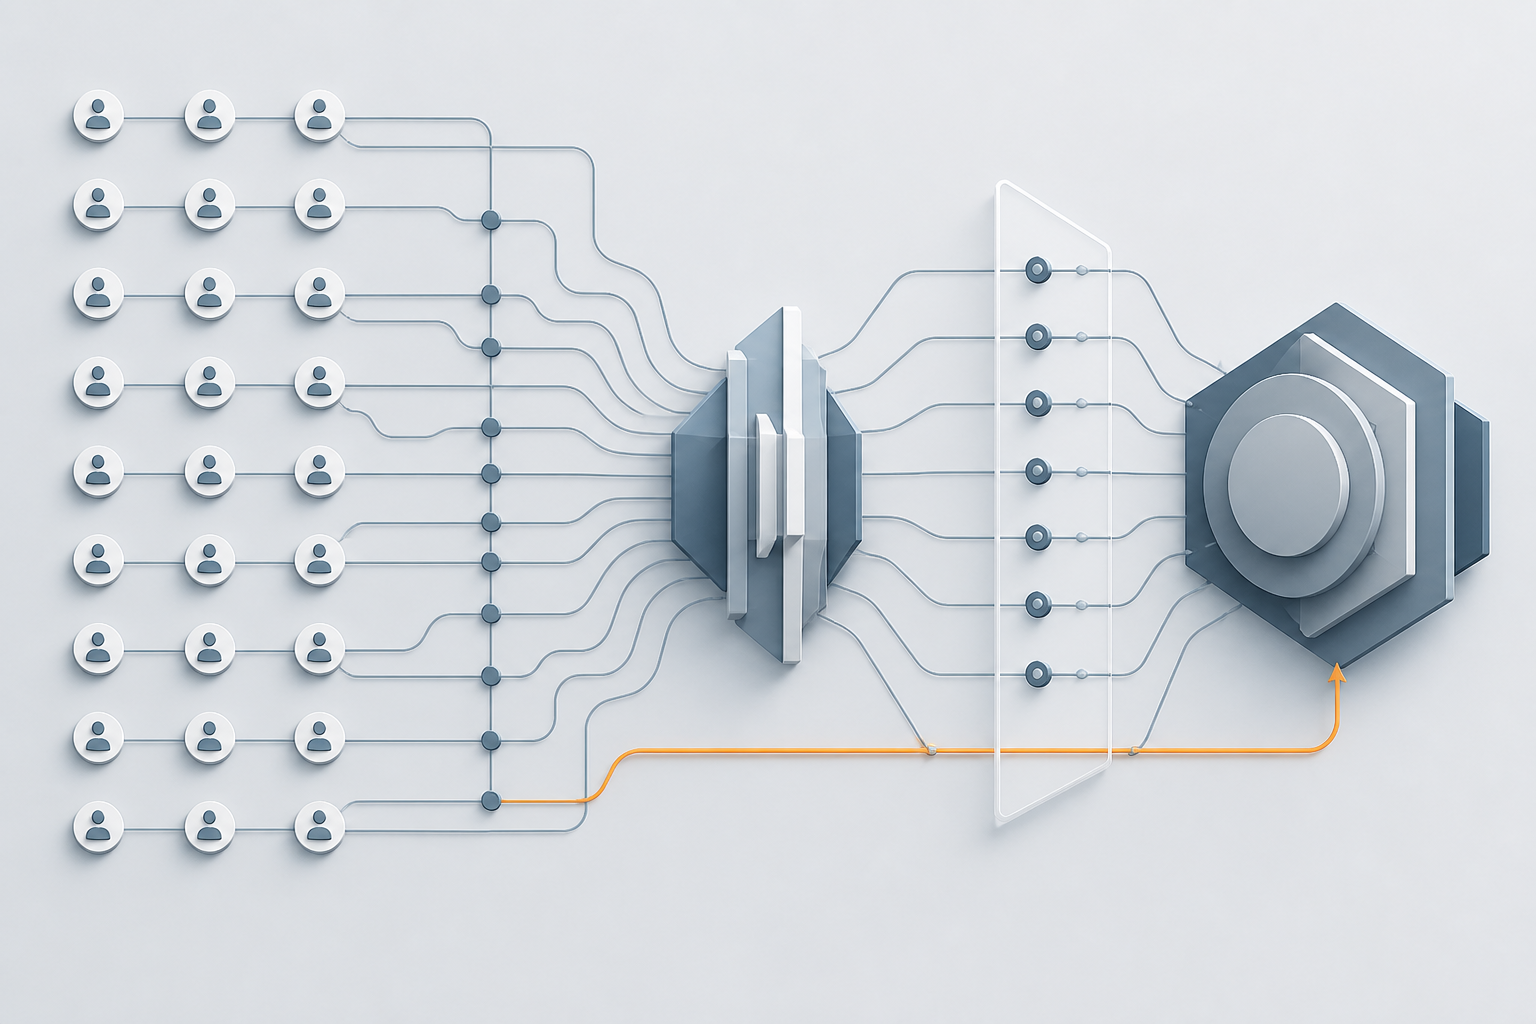
The lesson is not that attackers can generate enormous volumes of login attempts. They always could. The real issue is that an organization may have MFA, Conditional Access policies, and other visible controls in place while still leaving an authentication route where a password alone is enough.
For an SMB, that is as much a governance problem as a technical one. Partially deployed controls create a misleading sense of protection just as leaders are deciding where to direct limited IT and security resources.
Why Password Spraying Still Works
Password spraying differs from the familiar brute-force attack that tries thousands of passwords against one account. Instead, an attacker takes a small number of likely passwords—or credentials exposed in an earlier breach—and tests them across a large list of employee accounts.
The attacker moves slowly enough to avoid conventional account-lockout thresholds. Employee email addresses may come from public websites, LinkedIn, phishing campaigns, or prior data leaks. Attackers then test common passwords, company-related terms, or username-and-password combinations exposed in unrelated breaches.
This works when employees reuse passwords or when old passwords remain active after a third-party breach. A successful login may lead to email fraud, payroll changes, invoice scams, customer-data theft, ransomware access, or further credential theft.
In the campaign observed by Huntress, the attackers appear to have combined broad password spraying with known breached credentials. That makes each successful login more valuable. A working business account is not just access to one inbox. It may be a verified credential that can be sold, used for business email compromise, or leveraged to reach cloud data and administrative functions.
Huntress did not observe follow-on activity after the compromises associated with this campaign. That does not make the event harmless. Credential validation has commercial value, and a quiet attacker may be building an inventory for later use or resale.
The Problem Was Not Simply Missing MFA
Of 23 affected organizations examined by Huntress, eight had no MFA at all. That is a straightforward exposure.
The more revealing finding involved the other 15 organizations. They had MFA, but it did not apply to the sign-in method the attackers used.
The attack abused Resource Owner Password Credentials, or ROPC, a legacy OAuth authentication method. Unlike modern interactive sign-in processes, ROPC sends a username and password directly to a token endpoint. It does not support the normal MFA prompt or single sign-on experience. If that pathway remains available and policy does not block it, a valid password can effectively bypass the protection leadership believes MFA provides.
“MFA enabled” is not the same as “MFA required for every way an account can authenticate.”
Conditional Access policies in Microsoft environments can be highly effective, but only when their scope and enforcement are complete. Policies may cover only certain applications, groups, or users. They may exempt trusted locations. They may remain in report-only mode during a transition and never be fully enforced. They may not cover older or noninteractive client authentication methods.
Some exceptions are necessary during legitimate migrations. They also become durable attack paths unless someone is responsible for reviewing and removing them.
Stop Treating This as an IP-Blocking Problem
The campaign also shows why blocking suspicious IP addresses is necessary but insufficient. The observed activity moved through infrastructure providers and used bring-your-own-IP services, which allow customers to route traffic through address ranges they control. Attackers can switch providers and address ranges quickly.
IPv6 makes the problem harder. Its vast address space gives attackers far more addresses from which to operate, reducing the practical value of blocking a limited set of source IPs. A defensive strategy built mainly around blocklists becomes an expensive game of whack-a-mole.
The priority for SMBs should be making stolen or reused passwords less useful—not trying to identify every hostile machine before it connects. Authentication controls should assume that attackers will eventually obtain some valid employee passwords.
What Leadership Should Do
Ask the team responsible for Microsoft 365, Entra, or Azure administration a narrow question:
Can any user authenticate with only a username and password through a legacy, noninteractive, or excluded sign-in flow?
Request evidence, not a general confirmation that MFA is enabled.
The review should include Conditional Access scope across all users, cloud applications, and relevant client application types. It should identify excluded users and applications, trusted-location exceptions, report-only policies, and legacy authentication methods. The objective is not necessarily to eliminate every exception immediately. It is to document each one, assign a business owner, and establish an expiration date or remediation plan.
Disable ROPC and other legacy authentication methods unless there is a documented business dependency. If an application still relies on ROPC, treat it as a modernization risk with a specific replacement plan. A legacy integration should not quietly determine the security posture of the entire organization.
Limit Azure CLI access to employees who genuinely need Azure administration capabilities. Most staff do not. Restricting administrative tools reduces the number of accounts and pathways that could be valuable to an attacker.
Finally, improve password resilience. MFA remains the primary barrier, but unique passwords and a password manager reduce the chance that credentials exposed elsewhere will work in your environment. Where practical, move toward passwordless authentication or phishing-resistant MFA for administrators and high-risk users.
Security controls should be measured by the access they actually prevent, not by whether they appear on a policy document. MFA is powerful when it is consistently enforced. When coverage has gaps, attackers need only find one route where the password is still the key.